Enterprise Event Tech Security Checklist
The questions your security team will ask about any event platform. Written so you can hand it to them.
Cover of the Enterprise Event Tech Security Checklist
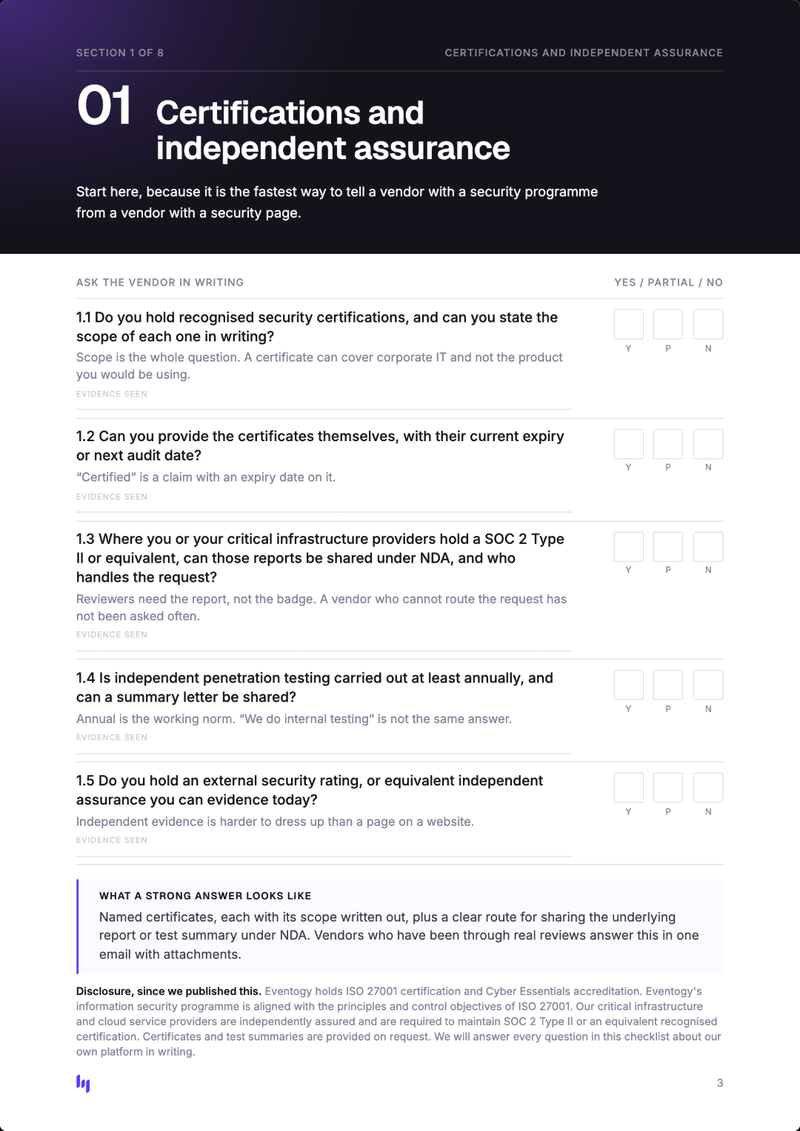
When an events team chooses a platform, the review that decides it usually happens in another department. This checklist is for that review.
It is written for IT, information security and risk reviewers, and it is vendor-neutral. It names no product, including ours. Every question is one a security reviewer would ask of any corporate event platform, and each section says what a weak answer looks like.
Who it is for. Heads of Events and events managers at banks and law firms who want to walk into a vendor review already knowing what will be asked. And the reviewers themselves.
Eight sections
- 01Certifications and independent assurance
- 02Hosting, data residency and encryption
- 03Identity and access: single sign-on, multi-factor, roles and permissions
- 04Data retention and what happens at the end of a contract
- 05Personal data: guest data, dietary and accessibility information, subprocessors
- 06Integrations, exports and where the data goes
- 07Audit trail: who did what, and whether you can see it yourself
- 08Incident response, resilience and continuity
Plus a red-flags page and a one-page scoring summary.
Ten questions to ask any event platform before you sign
Answer for the platform you use today, or the one you are about to choose. Two minutes.
1 of 10
Can they show you the security certificate, not just say they are aligned with it?
Aligned with ISO 27001 and certified to ISO 27001 are different sentences. Only one of them can be checked.
Just want the checklist?
Three fields and it is on its way, with the ten questions alongside it.
Published by Eventogy. ISO 27001 certified and Cyber Essentials accredited. We are happy to answer every question in this checklist in writing.
Read next
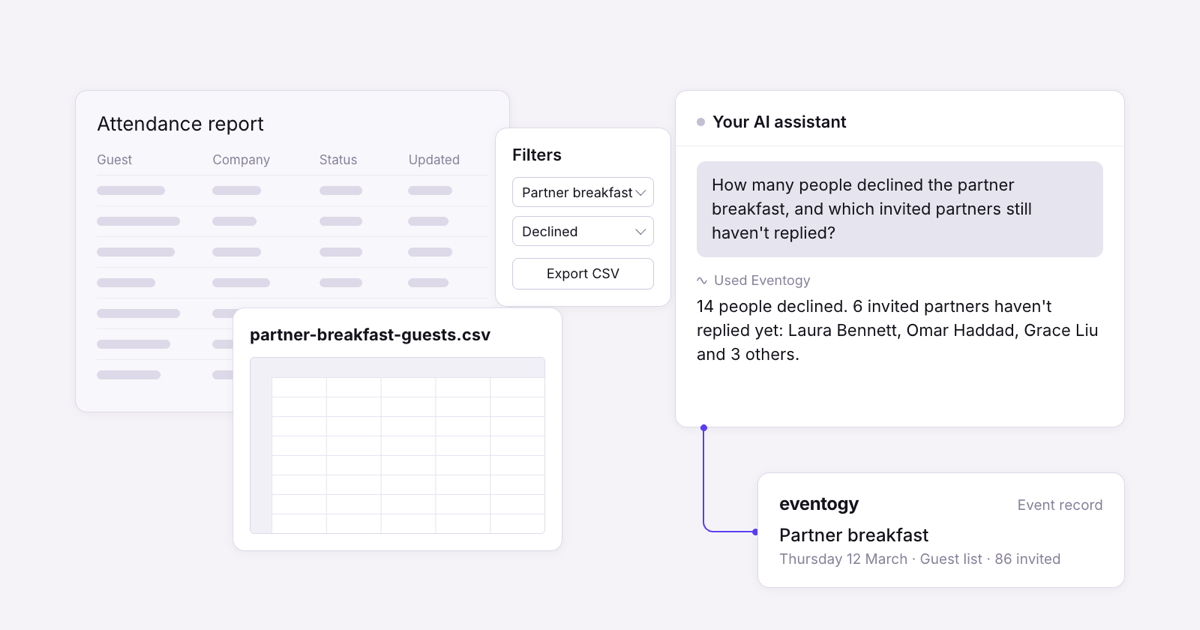 Connecting Eventogy to AI AssistantsThe developer building it explains how events teams will be able to ask their own assistant for answers from Eventogy, and what it was built not to do.
 Kieran Duff5 Oct 20265 min readYour event ended on Thursday. The questions started on Friday.A three-day event runs without a hitch, then one question lands: who came in on day two? Cem Kocu on why proving an event is now part of the job.
 Cem Kocu28 Sep 20266 min readWhy choosing event software is the easy partChoosing a platform takes weeks. Buying it takes a year. Why event management software purchases stall inside banks and law firms, and what moves them.
 Tom Phillips7 Sep 20265 min read
Or see how a platform answers all ten on screen: book a walkthrough